Close Menu
Newsweek ArabiaNewsweek Arabia
    Latest Posts

    Taking supplements your body doesn’t need? UAE doctors warn of health risks

    November 15, 2026

    Dubai Games to return for eighth edition in March 2027

    November 15, 2026

    Sheikh Mansoor bin Mohammed congratulates UAE athletes on historic Olympic achievement

    November 15, 2026
    Facebook X (Twitter) Instagram
    Newsweek ArabiaNewsweek Arabia
    Facebook X (Twitter) Instagram
    • Home
    • UAE
    • Business
    • Technology
    • Lifestyle
    • Sports
    Newsweek ArabiaNewsweek Arabia
    Home»Business»Microsoft finds active phishing campaign exploiting service disruption
    Business

    Microsoft finds active phishing campaign exploiting service disruption

    Editorial teamBy Editorial teamNovember 14, 2026
    Facebook Twitter Pinterest LinkedIn Tumblr Reddit WhatsApp Email
    Share
    Facebook Twitter LinkedIn Pinterest WhatsApp Email


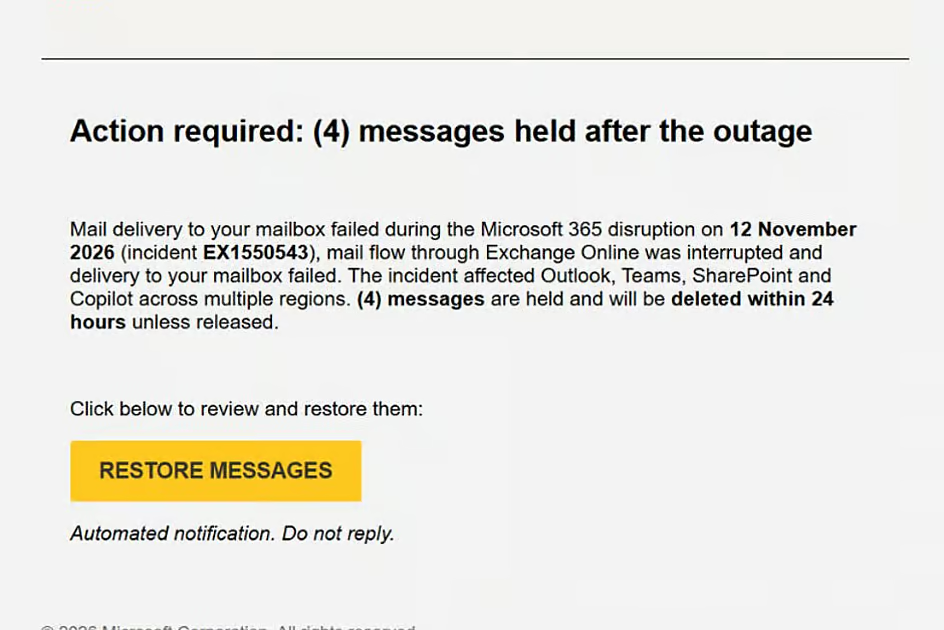
    Microsoft Threat Intelligence on Saturday found that an active phishing campaign was exploiting the Microsoft 365 service disruption on November 12.

    The messages, it said, impersonate notifications from Microsoft, referencing legitimate Exchange Online incident EX1550543. “Some of the phishing emails Microsoft detected on November 13 falsely claim that messages were held during the outage and will be deleted within 24 hours unless recipients click to restore them.”

    It said that observed subjects follow the pattern “Outage – [six-character code],” with sender display names using organisation-specific prefixes followed by “Outage Notification” or “Service Health.”

    Stay up to date with the latest news. Follow KT on WhatsApp Channels.

    The campaign uses three sender domains, moments-notice[.]com, planetmaison[.]com, and newbooker[.]com, with recipient-specific SendGrid click-tracking links redirecting to reallifeaccounting[.]com, including the observed path /themelist0.html.

    It said that similar messages targeted organisations across multiple US sectors, adding that activity is consistent with credential phishing. It also said that credential collection and malware delivery have not been confirmed.

    “Security teams can use Microsoft Defender for Office 365 Threat Explorer and Microsoft Defender XDR advanced hunting (EmailEvents, EmailUrlInfo, and UrlClickEvents) to identify suspicious messages, examine embedded URLs, and investigate user clicks.”


    Source: Khaleej Times

    Related Posts

    UAE, Mozambique expand trade cooperation at high-level business roundtable

    November 14, 2026

    Thousands of US flights canceled, delayed as air travel system recovers from shutdown

    November 14, 2026

    Dubai Chambers launches Quality Performance Lab for business excellence

    November 14, 2026
    Don't Miss
    Lifestyle

    Taking supplements your body doesn’t need? UAE doctors warn of health risks

    By Editorial teamNovember 15, 2026

    As temperatures ease and outdoor activities become more practical, residents across the UAE are getting…

    Dubai Games to return for eighth edition in March 2027

    November 15, 2026

    Sheikh Mansoor bin Mohammed congratulates UAE athletes on historic Olympic achievement

    November 15, 2026

    Up to 20% off across multiple brands as Dubai Police renew Esaad partnership with GMG

    November 15, 2026
    Our Picks

    Taking supplements your body doesn’t need? UAE doctors warn of health risks

    November 15, 2026

    Dubai Games to return for eighth edition in March 2027

    November 15, 2026

    Sheikh Mansoor bin Mohammed congratulates UAE athletes on historic Olympic achievement

    November 15, 2026

    Up to 20% off across multiple brands as Dubai Police renew Esaad partnership with GMG

    November 15, 2026
    Facebook X (Twitter) Instagram Pinterest
    • UAE
    • Business
    • Technology
    • Lifestyle
    • Sports
    • Contact us
    2026. All rights reserved.

    Type above and press Enter to search. Press Esc to cancel.