
Ned Baltagi of SANS Institute highlights critical gaps in AI governance, emerging cyber threats, and the specialised skills needed to secure AI-driven enterprises across the Gulf
Rapid adoption of artificial intelligence across the Gulf is creating new opportunities for innovation while exposing organisations to increasingly complex cybersecurity risks. Despite growing investments in AI, gaps in governance, threat detection, data protection and workforce capabilities continue to challenge enterprise security readiness.
With AI becoming embedded in government services, financial institutions, energy operations and critical infrastructure, organisations face mounting pressure to strengthen security frameworks and develop specialised expertise. SANS Institute’s AI Security Maturity Model offers a structured approach to assessing organisational readiness across protection, utilisation and governance, helping enterprises identify vulnerabilities and align AI security strategies with operational and regulatory requirements.
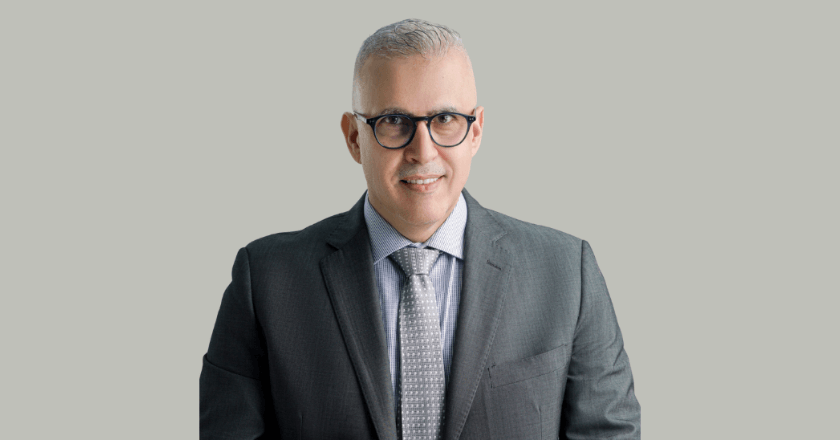
In an interview with TahawulTech, Ned Baltagi, Managing Director of Middle East, Africa and Turkey at SANS Institute, discusses the region’s AI security maturity, emerging threats posed by autonomous AI agents, governance priorities and the growing importance of hands-on cybersecurity training in building resilient AI environments.
Interview excerpts
What does the SANS AI Security Maturity Model reveal about AI security readiness and common gaps among organisations in the Gulf?
AI adoption across the Gulf is accelerating, particularly in government, financial services, energy and critical infrastructure. However, security capabilities and governance are not always advancing at the same pace. The SANS AI Security Maturity Model assesses organisations across three pillars — Protect, Utilise and Govern — and five maturity stages, helping security leaders identify gaps between their AI ambitions and operational readiness. Common challenges include limited visibility into AI deployments, inadequate controls around sensitive data, and insufficient oversight of AI models and automated systems. Governance is particularly important. The model emphasises that organisations cannot achieve sustainable AI security maturity without documented policies, clear accountability and measurable controls.
For Gulf enterprises, the priority is moving beyond AI adoption strategies towards evidence-based security programmes aligned with business risk and regulatory requirements. The Gulf Edition provides a framework for this assessment.
How can organisations strengthen governance across the development, deployment and use of AI systems?
Effective AI governance must cover the entire lifecycle, from model selection and development through deployment, monitoring and eventual retirement. Organisations should establish a comprehensive inventory of AI systems, classify the data they process, assign accountable owners and implement risk-based security assessments before production deployment. This includes addressing third-party models, shadow AI, access permissions and the growing autonomy of AI agents. The SANS AI Security Maturity Model identifies five essential governance capabilities: AI policy, risk management, oversight and accountability, visibility into shadow AI and bring-your-own-AI usage, and compliance readiness. Frameworks such as NIST AI RMF and ISO/IEC 42001 provide supporting structures, but governance must translate into practical, auditable controls. Effective governance enables organisations to embrace AI innovation while maintaining strong security, accountability and confidence in its adoption.
How is the AI cybersecurity skills gap affecting regional resilience, and which capabilities should security teams prioritise?
The AI cybersecurity skills gap presents a significant challenge because organisations need professionals who understand both traditional cyber threats and the vulnerabilities introduced by AI systems. SANS’ 2026 global research found that 73% of practitioners reported changing training requirements because of AI, highlighting how quickly workforce demands are evolving. For Gulf organisations investing heavily in digital transformation, this creates an urgent need to develop specialised capabilities alongside technology adoption. Security teams should prioritise AI application security, model and data pipeline protection, adversarial testing, AI governance and the practical application of AI within security operations. Equally important is developing the ability to identify prompt injection, insecure integrations and AI-generated threats. Building these capabilities through role-based training and practical assessments will help organisations strengthen resilience while reducing dependence on a limited pool of specialised talent.
What emerging threats pose the greatest risks to AI applications and critical infrastructure, and how should organisations address them?
The most pressing threats include prompt injection, data leakage, malicious third-party models, supply-chain vulnerabilities and the misuse of autonomous AI agents. SANS’ 2026 global research found that 78% of respondents reported confirmed or suspected AI-enabled attacks, while 63% identified significant shortcomings in AI threat detection and response. As AI becomes integrated into critical infrastructure, these risks extend beyond data confidentiality to operational continuity and potentially physical safety. Organisations should adopt a defence-in-depth approach that includes secure model development, supply-chain validation, adversarial testing, continuous monitoring and strict access controls. For agentic AI, SANS emphasises the Principle of Least Agency, ensuring autonomous systems receive only the permissions and authority necessary to perform their tasks.
In critical infrastructure environments, human oversight, operational safeguards and clearly defined intervention procedures are essential to preventing AI-related failures from escalating into wider disruptions.
How can hands-on training and specialised skills help organisations build secure and resilient AI environments?
Building AI resilience requires more than awareness training or theoretical knowledge. Security professionals need practical experience identifying vulnerabilities, securing AI development pipelines, testing models against adversarial attacks and responding to incidents involving AI systems. Hands-on training enables practitioners to apply these capabilities in realistic environments, helping organisations turn security policies into effective operational controls. SANS supports this approach through specialised courses such as SEC545: GenAI and LLM Application Security, which includes 20 hands-on labs covering prompt injection, AI agents, RAG security and MLOps, alongside the GIAC AI Platform Security (GAIPS) certification. Courses such as SEC546: Securing Agentic AI and SEC598: AI and Security Automation for Red, Blue, and Purple Teams address further specialised capabilities. For Gulf organisations, investing in practical, role-based training is essential to developing local expertise, strengthening cyber resilience and enabling AI innovation securely and sustainably.
Source: Tahawul Tech